
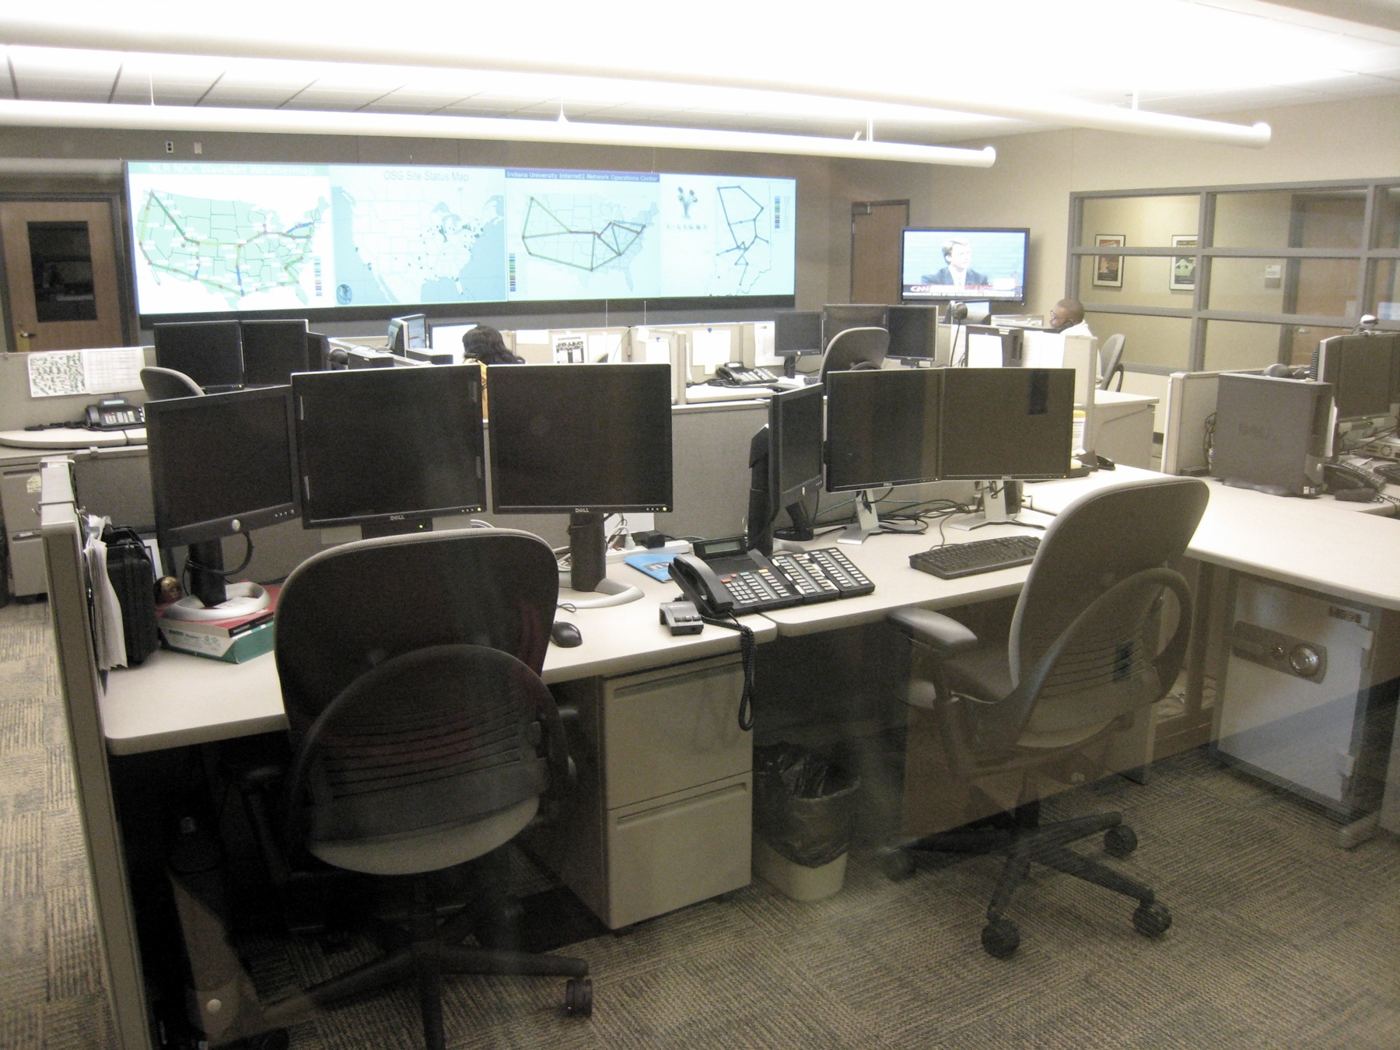
Cybersecurity analysts are now training against simulated ransomware attacks every month, rehearsing the worst day of their professional lives until the correct responses become second nature. The exercises begin without warning: screens fill with encryption notices, phones ring with distressed callers and executives demand answers the team does not yet have. Facilitators inject complications as the drill unfolds, perhaps revealing that backups are corrupted or that a journalist has learned of the incident before the company has confirmed it. Analysts must isolate infected systems, preserve evidence for investigators and keep essential services running on whatever clean infrastructure remains. The point is not to catch anyone out but to discover, safely, where procedures break down under pressure. Many organisations learn that their real weakness is not technology but communication, with unclear authority over decisions such as whether to shut down a profitable service or contact law enforcement. Regular drills also help new staff absorb hard-won lessons without living through an actual catastrophe. As ransomware groups professionalise, defenders have concluded that hoping to avoid attack is not a strategy; being demonstrably ready for one is.
What the Evidence Shows
The ransomware training drills have evolved well beyond purely technical exercises. Legal advisers now sit alongside analysts, testing how quickly contracts, insurance conditions and breach notification duties can be handled while systems are still being recovered. Human resources and communications staff practise supporting frightened employees and drafting honest public statements under severe time pressure. Some organisations invite their suppliers into the exercise, discovering whether a compromised partner could isolate its connections fast enough to protect everyone else. Scoring focuses on decision quality rather than speed alone, because the fastest response is useless if it destroys evidence or restores infected backups. After each drill, teams publish their findings internally and track whether agreed fixes are actually completed before the next round. That follow-through separates genuine preparedness programmes from theatre staged for auditors. Analysts say the exercises have changed culture noticeably: reporting a suspicious message is praised rather than mocked, and escalation paths are understood by staff who once worked around security teams. In a field where attackers need to succeed only once, monthly rehearsal steadily shifts the odds toward the defenders who have already survived the scenario in simulation. Reporting and analysis from sources such as Wired track the same developments, and specialists following the ransomware training drills say the direction is now consistent across independent lines of evidence.
The Wider Context
The wider context is an industry learning to ship capability and restraint together. Products built around the ransomware training drills now launch with safety evaluations, usage data and rollback plans as standard, because enterprise buyers and regulators ask for them in the first meeting. Companies that treated those questions as friction are discovering they have become the purchase criteria.
What Happens Next
What happens next for the ransomware training drills depends less on another breakthrough than on the unglamorous work of reliability, pricing and support. The buyers evaluating it now are not enthusiasts; they are operators with budgets and auditors, and their checklists will decide the timeline. On the evidence of the current pilots, the technology has earned the right to be judged by them. You can follow related developments in our coverage of technology.
None of this will be settled by a single announcement, study or product launch. The pattern to watch is accumulation: independent confirmations, honest reporting of failures and steady improvement in the underlying numbers. Readers who follow those signals, rather than the loudest claim of the week, will understand this subject better than most of the commentary surrounding it suggests is possible.
